SNI is a name your device often sends while TLS is starting. It is not the page. It is not the password in the form. It is a hostname, sent so a server that hosts many sites knows which certificate to pull. On a cafe path without a tunnel, that name can sit in the clear even when the rest of the session is modern. People hear HTTPS and stop listening. The padlock is real. The name is a different leftover.
A VPN still wraps the path from your device to a server you picked. Wikipedia's VPN page is the noun. RFC 8446 is TLS 1.3 on the website. It is not a tunnel, and it is not a promise that SNI vanished. Cloudflare also keeps a what is SNI explainer if you want the virtual-host reason in someone else's words. Encrypted Client Hello exists in the industry. Deployment is uneven. Do not claim the cafe sees nothing.
This is not VPN vs HTTPS in Plain English: Two Locks, Two Hops. That URL is two locks, two hops, padlock versus tunnel as a pair. SNI shows up there as one leftover. This page is the leftover: why the name exists, what a capture still shows, why ECH is not a cape, why the IP hop remains when the letters get quieter. This is not the VPN on Cafe Wi-Fi: A Habit, Not a Superpower. Splash pages and kill-switch deadlock live there. SNI is one row in that shop, not the plot. This is not What DNS Does on a VPN (Plain English). A DNS question is a different packet from a TLS name. They look similar in English. They are not the same hop.
KloxVPN is WireGuard, OpenVPN, OpenConnect, and Shadowsocks, five devices, yearly from $2.83 a month, 7-day money-back on first purchase. Features lists DNS through the tunnel, IPv6 leak protection, WebRTC leak blocking. There is no consumer custom-DNS picker in this article. There is no city count. Download is the apps. Pricing is the live number. The cookie page is how this website treats cookies. SNI is not a cookie, and a cookie policy is not a handshake.
I have a bias. Treat clear SNI as a map the local network can read. Treat ECH as real where it actually runs, and incomplete everywhere else. Add a tunnel when that map is a problem you have. Do not wait for the industry to finish hiding names. Do not skip the padlock because you bought a hop.
Related reading: White-Label VPN and Terms Mistakes and Xsave: Not a Mitigation Toggle. Xsave64: Not a Mitigation Toggle and Xsavec vs a VPN: Practical Notes. What is a VPN? and VPN kill switch.
Looking for a reliable VPN?
KloxVPN — from $2.83/month. Apps for every device.
A name during handshake
A lot of websites share a box. One IP, many hostnames, many certificates. The client has to say which name it wanted before the server can pick the right cert. That sentence is Server Name Indication. Historically the name rode in the ClientHello in the clear. The rest of TLS could still wrap the page. The name had already left the building.
You do not need a lab to use the idea. You need to stop treating 'encrypted website' as 'nobody learned which website.' The cafe radio, the hotel concentrator, your ISP, a bored roommate with Wireshark: they can often read the letters. They cannot read the inbox. Those are different sentences. Farms mash them because both sound like 'they can see me.' Split them.
The name exists for an operational reason, not a surveillance reason. Shared hosting and CDNs need it. Turning it off on the open web would break a pile of certificates. Encrypted Client Hello is the industry's attempt to hide more of that first flight. It is not a consumer toggle in Klox. It is a browser, CDN, and origin story. I will not pretend our Connect button ships ECH for you.
If you already live in packet captures, you know the field. If you do not, you do not need to start now. Trust the split: page body versus hop metadata. SNI is metadata. A VPN moves metadata by making the cafe's interesting packet a blob to a node you chose. That is the whole product claim I will stand behind. I will not stand behind 'the cafe sees nothing.' Volume, timing, and the fact you used their AP remain. The name is what this page exists to name.
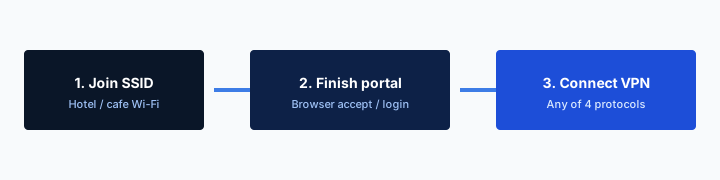
- 1Skim the seating / order diagram.
- 2Do the numbered steps once on your real network.
- 3Use the FAQ if a sentence was too long.
- 4Follow one related article — not ten tabs.
How to read this page
| Observer | Page body on HTTPS | SNI if still clear | IP hop | With Klox connected |
|---|---|---|---|---|
| Cafe LAN | No, if TLS is real and the host is the one you meant | Often yes | Yes | Sees a blob to a VPN; not the inner name |
| Home ISP | No on TLS sites | Often yes | Yes | Sees a blob to a VPN |
| The website | Yes, it is the site | It already knew the name | Sees your IP, or the VPN exit if you tunneled | Sees the exit IP and a normal TLS session |
| ECH actually running | Still TLS | Name quieter on that path | Still yes | Tunnel still moves the outer hop |
| Cookie on klox.app | Unrelated | Unrelated | Unrelated | See /cookie; neither is a handshake |
HTTPS already locked the page. The cafe can still see a name and an IP unless that hop is a VPN.
— KloxVPN consumer notes
Cloudflare Learning: What is a VPN?
Virtual hosting is why the name exists
One box, many sites, many certs. The client has to say which site. That is operations. It became a privacy leftover because the letters used to travel in the clear. ECH tries to shrink that leftover. It has not finished the job on every path you actually use.
What this post is not
Not the two-locks essay. Not cafe splash timing. Not a DNS leak procedure. Those URLs exist. This URL is the hostname during TLS start until you can say it without mixing it with the padlock.
HTTPS already locked the page
RFC 8446 is how a lot of the public web encrypts the session. Mail web UIs. Banks. Work chat. Stores. The waiter with a laptop is not reading your password from those TLS records if the certificate matches the host you meant. That fight is mostly over. Farm copy still writes as if 2012 HTTP were the default. It is not. If your scare is the page body on cafe Wi-Fi, check the padlock first.
The leftover after you grant TLS is quieter. Destination IP. Often the server name in SNI. DNS if names never entered another wrap. That is a map of who you talked to. It is not the email. People who say 'I have HTTPS so I do not need a VPN' are often talking about the email and forgetting the map. People who say 'HTTPS is fake' are often selling a tunnel with a scare that 2012 already retired. Both pitches skip the name.
I will not crown a winner. The two-locks article already refused that game. Here the job is narrower: admit the page is locked, then look at the name. If you cannot hold both facts, you will either skip a hop you wanted or buy a cape you do not need.
Certificate warnings are still your job. A tunnel encrypts a mistake as happily as a real bank. The padlock on a host you did not intend is not the padlock you wanted. SNI on a lookalike domain is still a name. It is the wrong name. Phishing is a lie you believed. Encryption of a lie is still a lie. I will not turn this into a PKI course. Trust the browser's name match. Do not install a cafe's extra root because a PDF said Wi-Fi required it.
Padlock versus letters
Padlock: page body. Letters: SNI, often. Numbers: the IP. A VPN moves letters and numbers off the cafe path. It does not replace the padlock. Keep both.
Warnings still win
If the browser yells, stop. Complete a splash on a boring site if you must. Come back to the bank with a lock you trust. SNI trivia will not save a click-through.
The IP hop remains
Hide the letters and you still have numbers. You opened a connection to some address for some number of minutes. An observer who already knows who lives at that address does not need SNI. A small site on a dedicated IP is a name in all but spelling. A huge CDN anycast IP is quieter: many names share the number, so the number is a neighborhood, not a doorbell. Do not pretend every IP is a neighborhood. Do not pretend every IP is a doorbell. Reality is mixed. Plan for mixed.
Encrypted Client Hello, when it actually runs, shrinks the name. It does not delete the TCP or QUIC session to an IP. Volume remains. Timing remains. A four-hour fat blob is still a four-hour fat blob through a VPN too. The tunnel changes who the cafe thinks you talked to. It does not make you look idle.
This is why 'ECH shipped, so I uninstalled the VPN' is a bad slogan. ECH is uneven. IPs remain even when ECH is perfect. A VPN still collapses the outer hop to 'talk to the VPN' from the cafe's chair. That sentence is true whether SNI is loud, quiet, or gone on that particular site.
I will not invent city counts so the map sounds fancier. You pick a server in the app. Nearby is usually enough when the job is 'hide this hop from the shop,' not 'pretend I live in a catalog.' Catalogs are a different article. This one is numbers that survive a hidden name.

Shared IP is not invisibility
Many names on one anycast address make SNI more interesting than the number. A lonely IP makes the number enough. You do not get to pick which kind of host you visited. A tunnel covers both cases from the cafe's point of view.
Volume is still metadata
Encrypting a hop does not shrink a 4K stream into a blink. If your threat watches sizes, plan for that. Most cafe threats do not. Most ISP graphs still like names and IPs more than byte counts.
ECH without theater
Encrypted Client Hello is the industry name for hiding more of the TLS ClientHello, including the server name, from the path. Browsers, CDNs, and origin configs have to agree. Some paths have it. Some do not. Some have it on Tuesday and not on a corporate middlebox that still wants to see names. Do not write 'SNI is dead in 2026' because a blog said ECH exists. Do not write 'SNI always dooms you' as if ECH never ships.
I will not perform handshake theater. No screenshots of extensions lists. No draft numbers you have to memorize to use Klox. If you want to see SNI on your own LAN, you already know Wireshark. If you do not, you do not need to. The consumer fact is: assume the name might still be visible on a clear path. Assume a tunnel still earns its keep when the name is hidden, because IPs remain.
Klox does not claim to implement ECH for you. ECH is a browser-and-CDN story. The tunnel is a device-to-node story. Keep them in separate drawers. Mixing them is how you get a ticket that says 'why is SNI still a thing if I paid for a VPN.' Because SNI lives inside the inner TLS after you decrypt at the node, or on the clear path if you never tunneled. The cafe does not get the inner SNI when the tunnel is up. The path from the VPN node to the site still does TLS like everyone else. That inner name is not the cafe's problem anymore. It is a hop-operator fact, same as any other HTTPS client on the internet.
RFC 8446 is TLS 1.3. ECH rides later work. You do not need the draft to tap Connect. You need to stop treating the address-bar lock as a complete privacy product, and stop treating a press release about ECH as a uninstall-the-app event.
Uneven means uneven
Some clients, some CDNs, some days. A site that supports ECH in one browser may still show SNI in another. Plan as if the name might leak on the clear path. Plan as if the tunnel still matters.
Inner TLS still has a name
The VPN node is not the website. After the tunnel, you still speak HTTPS to the site. That inner handshake still has a hostname. The cafe does not sit on that inner hop when you are connected.
DNS leftover, not this essay
HTTPS can hide page bodies and still leave names on the floor if DNS never entered a tunnel. You type a host. The stub resolver asks someone what IP that is. Off a VPN, that someone is often the ISP or the cafe router. That question is a shopping list. SNI is a later name, during TLS start, to the IP you already learned. Two names, two moments. People mash them because both are letters.
On a VPN, if the client is doing the job Klox documents, DNS rides the tunnel. The ISP sees a blob to the VPN, not the list. That leftover is why What DNS Does on a VPN (Plain English) exists. I will not rewrite the resolver plot. I will say: hiding SNI does not hide a clear DNS query that already happened. Encrypting DNS with browser DoH to a third party does not hide the IP you later connect to. Different envelopes. The DoH essay is a sibling if you wanted that fight. This page stays on the TLS name.
Do not stack a public resolver, browser DoH, and tunnel DNS as vitamins. One owner for names while the tunnel is up. Klox is that owner on our apps. We are not selling a custom-DNS picker here. If a farm tells you to type 1.1.1.1 into the adapter 'for speed,' that farm is teaching a different leftover. That leftover can undo tunnel DNS on purpose.
IPv6 can be another leftover: a v6 path that never entered a v4-only tunnel. WebRTC can ask STUN for a public IP while the UI says connected. Features lists protections. This is still not the leak-test article. It is why 'HTTPS finished the job' is the wrong slogan even after you grant TLS, and why 'ECH finished the job' is the wrong slogan even after you grant a quieter ClientHello.
DNS is earlier, SNI is later
Question to a resolver, then connect, then TLS start. Hide one leftover and the other can still talk. A tunnel that owns both is simpler than collecting wraps.
Do not collect resolvers
Browser DoH plus VPN DNS plus a random adapter IP is how you get a leak you cannot draw. One owner while connected. Then stop.
What a tunnel changes
With Klox up, the interesting hop for the cafe and the ISP becomes the VPN server. They still know you used the AP. They still see volume. They see a destination you chose when you picked a node. They do not get the inner map of sites unless something leaked around the tunnel: DNS, IPv6, WebRTC, an excepted app, a second NIC. Features lists tunnel DNS, IPv6 leak protection, WebRTC leak blocking. Confirm after connect if you like labs. Then stop collecting testers.
The inner SNI, the one in the TLS session from the node to the site, still exists. The cafe does not sit there. The VPN path still looks like a normal HTTPS client to the website, plus an exit IP that is not your house. The website still sees you logged in. A tunnel is not a new identity. It is a new first hop.
WireGuard first. OpenVPN when the AP hates UDP. Same SNI story on both protocols. Protocol hopping is not extra ECH. Five devices: phone plus laptop is two seats if both tunnels are up. The name-hide is per device. A tunneled phone does not hide SNI on a laptop that never connected. Count.
Smart Connect, if the app shows the row, is connect on untrusted Wi-Fi. It starts the hop that moves SNI off the cafe path. It does not encrypt ClientHello by itself. If the row is missing, you have a Connect button. Use the button. I will not invent an always-on lock so this article matches another vendor's screenshot.
Per device, not per cafe
Each gadget that joins the shop SSID needs its own tunnel if you care about that gadget's names. HTTPS will be there anyway. The hop lock is per NIC.
WireGuard, then OpenVPN
Same leftover physics. WireGuard is the default I want. OpenVPN is the spare tire when a rude AP blocks UDP. Switching protocols will not hide a name you never tunneled.
What a name-hide still cannot do
Hiding SNI from the cafe, whether by ECH or by a tunnel, cannot stop you from logging into a fake bank. It cannot scan the attachment. It cannot make the AP honest. An evil twin still gets your traffic. Encrypted, if the tunnel is up. The twin can still captive-portal you, still annoy you, still see that you spoke to a VPN. Encryption is not authentication of the coffee shop. Ask the staff the SSID.
It cannot hide that you are on that SSID. Shop logs, AP vendor, sometimes a camera over the till: those are not SNI problems. If your threat is a person in the room, sit differently. If your threat is the LAN graph, tunnel. If your threat is the site, that is the site.
It cannot replace unique passwords. It cannot replace updates. It cannot replace 2FA. The What a VPN Cannot Do catalog owns that list. I will not paste it. I will say: a quieter ClientHello on a phone full of reused passwords is a nicer hop for the same account takeover.
It cannot unlock a streaming catalog I did not promise. SNI trivia plus a VPN is not a Netflix product. If a farm said otherwise, they were selling a cookie. Klox is a tunnel, five devices, two protocols. Use it as that. It cannot be SOC 2 because a buyer likes logos. I will not invent an audit PDF in an SNI lesson. Consumer Klox is a hop. Cookies on this site live at /cookie and are not a handshake field.
Phishing still uses a name
A lookalike host has SNI too. TLS to the liar is still TLS to a liar. A tunnel does not approve the hostname. The browser's name match does. Read it.
The shop is not a certificate authority
The cafe does not issue Gmail's cert. A VPN node does not either. Trust the browser. Ask humans for the SSID. Those are different trust problems.
After connect, one leak test
If you want proof the hop moved, use the Leak Test After You Connect a VPN article. IP, DNS, WebRTC, IPv6 as a procedure. This page will not become that procedure. SNI is not a row on most consumer leak sites. Those sites show an IP and a resolver. They do not print your last ClientHello. Do not demand they do. If the IP is the VPN and DNS is the tunnel, the cafe's interesting hop moved. That is the check that pays rent.
Do it once on a network you control. Then stop. Daily labs are how people forget to live. If a test fails, fix the leftover: IPv6, WebRTC, a browser DoH override, an excepted app. Then test once more. Then drink the coffee.
Yearly from $2.83 a month is not a reason to skip the padlock. It is a reason you can afford the hop without a farm's lifetime coupon. Seven days on first purchase if the product is not the hop you wanted. Refunds live on /refund. Store purchases follow the store. This page will not turn into a billing sermon.
If you only needed the English, stop here. If you needed two locks as a pair, the HTTPS essay is next door. If you needed cafe timing, that habit post exists. If you needed the shopping list, DNS on a VPN owns it. If you needed a cape, you wanted a farm. NordVPN's HTTPS-versus-VPN post is a specimen of the mash. Use it as a specimen. Do not import their winner. There is no winner. There is a name, an IP, a padlock, and a tunnel you can turn on.
Leak sites do not print SNI
They print IP and DNS. That is enough to know whether the outer hop moved. Wireshark is how you see letters. Most people do not need Wireshark. Most people need Connect.
One afternoon, then stop
Download the apps. Connect on a guest SSID at home. Run one leak test. Notice that the cafe will not get your inner names. Then use the habit. Do not collect ClientHello screenshots as a personality.
Key Takeaways
SNI is a hostname sent while TLS starts. HTTPS already locked the page. The cafe and the ISP can still see that name when it is clear, and they can still see the IP even when Encrypted Client Hello hides letters. ECH is real where it runs. It is uneven. Do not claim the shop sees nothing.
A VPN moves the interesting hop to a node you chose. Klox is WireGuard, OpenVPN, OpenConnect, and Shadowsocks, five devices, yearly from $2.83 a month, seven-day first purchase. DNS through the tunnel. No city count. No custom DNS picker in this essay. Cookies on this site live at /cookie and are not a handshake.
If you wanted two locks as a pair, that essay is next door. If you wanted cafe timing, that habit post exists. If you wanted a leak procedure, that checklist exists. If you wanted the name, you have it. Download the apps. Connect on networks you do not run. Leave the padlock on. The name was never the page.
Related Resources
Move the name off the cafe path
KloxVPN is WireGuard, OpenVPN, OpenConnect, and Shadowsocks, five devices, yearly from $2.83 a month, 7-day first-purchase money-back. HTTPS already locked the page. SNI and the IP hop can still leak on the LAN. Download the apps if you want that hop to be a VPN.
Download KloxVPNFrequently Asked Questions
KloxVPN Team
Experts in VPN infrastructure, network security, and online privacy. The KloxVPN team has been building and operating VPN services since 2019, providing consumer and white-label VPN solutions to thousands of users worldwide.